


Australian supermarket giant Coles has enlisted cybersecurity experts to help secure its systems in the wake of a cybersecurity incident, although initial investigations suggest no customer data has been compromised.
On Monday morning, Coles told investors via the Australian Stock Exchange (ASX) that it was “investigating a cyber security incident”.
In a statement totalling less than 150 words, the supermarket giant stressed that its findings to date had not uncovered any evidence of “customer, team or supplier data” having been compromised or removed from Coles’ systems.
Coles did not specify when its investigations began, what the cybersecurity incident involved, or whether any known threat actor had been identified.
When approached for more information, a Coles media representative referred Information Age to the company’s ASX announcement.
“We don’t have anything further to add at this point,” they said.
The company did not specify what systems may have been affected, though Coles told the ASX “global cyber security experts” had been engaged to contain and secure the Coles IT environment.
The company said it is also working with the Australian Cyber Security Centre and will continue to “engage with appropriate agencies and regulators as investigations continue”.
Coles says keep shopping, workers report issues
Coles reassured customers that “operations continue” despite the incident.
“Customers are able to shop as normal with Coles in stores and online,” read Coles’ announcement.
In an FAQ section on its website, Coles acknowledged a “small number” of customers were experiencing issues with click-and-collect orders for its bottle-shop chain Liquorland.
On the r/coles subreddit – where Coles staff and shoppers anonymously discuss the supermarket chain – some users reported system issues were allegedly preventing them from processing stock counts or product markdowns.
“Fresh Produce didn't get half of their load in, and meat was missing a pallet or two as well,” wrote one user.
“Nothing working still, I can’t do nearly all of my normal daily tasks,” wrote another.
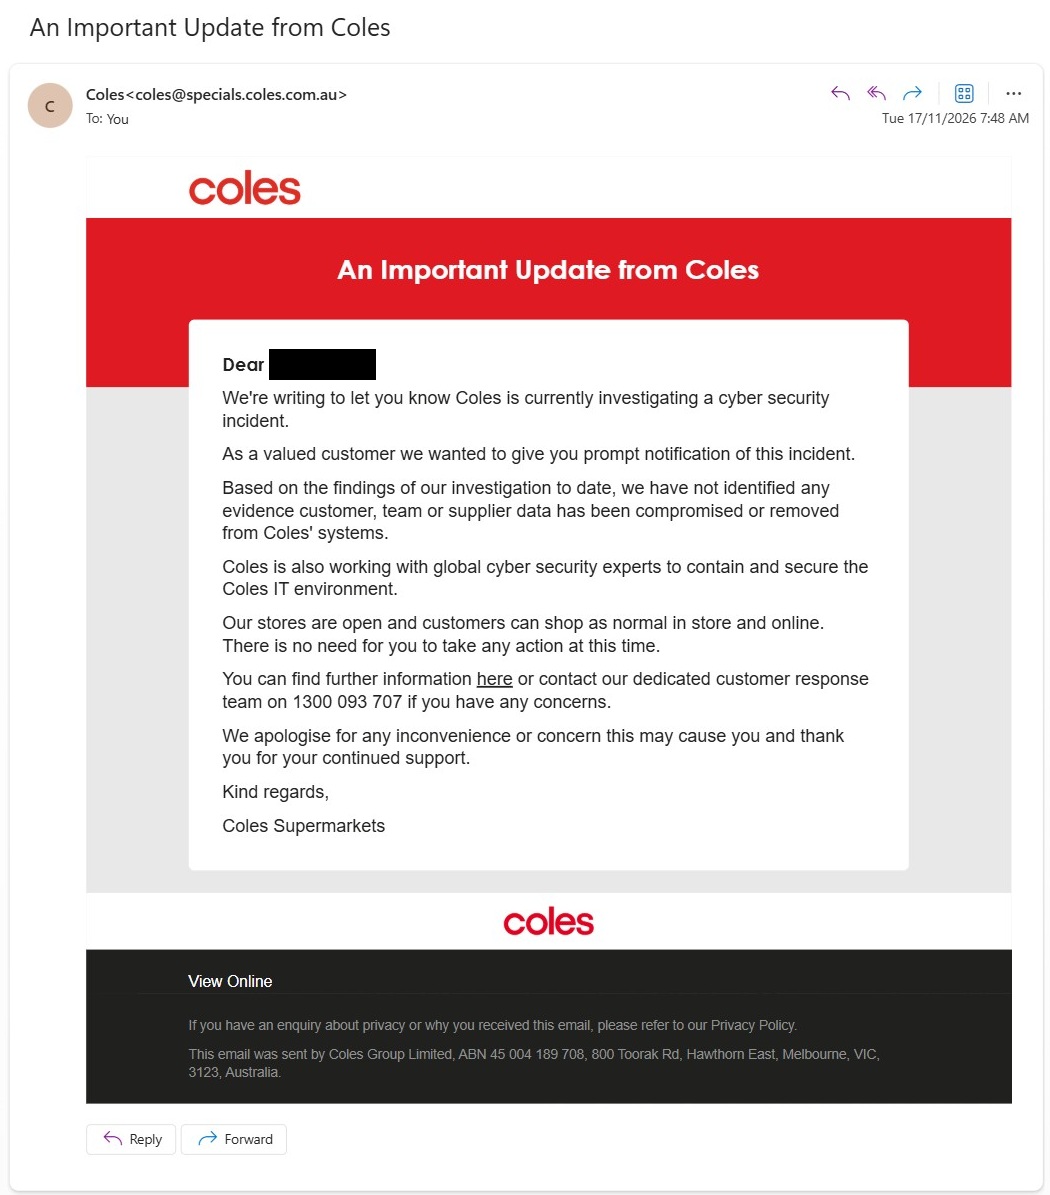
The email Coles sent to affected customers. Photo: Supplied.
Notably, Coles’ internal email system was one of many reportedly affected by a global outage at Microsoft on Friday, though general store operations continued as normal.
Coles has not announced any system outages as a result of its cybersecurity incident or Friday’s Microsoft outage.
Supermarkets under threat
The Coles incident comes amid growing concerns about the cybersecurity of supermarket infrastructure, following two waves of cyberattacks targeting refrigeration systems at European supermarkets during October and November.
Hackers reportedly targeted internet-connected controllers for supermarket fridges and freezers in at least 11 European countries, remotely switching refrigeration units into defrost mode.
Temperatures inside some units reportedly soared as high as 70°C, forcing supermarkets to discard food or temporarily remove products from their shelves.
France – which accused Iran of being behind the attacks – reportedly saw millions of euros worth of food discarded after some 700 stores were hit in early October.
The attacks have prompted global concerns about the security of supermarkets and food retailers, including those in Australia.
Following Coles’ announcement, the Australian Computer Society (ACS) called on Australia's major retailers to “test whether their people, not just their systems, are ready for a cyberattack”.
"Coles has moved quickly and been upfront, and that's the right response," said ACS chief executive Prins Ralston.
"But every retailer in the country should be asking itself the same question today: if this happened to us, do we have the people to contain it and keep trading?"
"The hackers in France got in through internet-facing equipment, default passwords and old systems that no longer got updates.
"It happened overnight, the alarms didn't go off and there was no one on site to notice.So, Australians, ask the hard questions now. If the fridges failed at 2am, who would spot it?
“Who has the authority to act? And how would the stores open the next morning?"
Coles acknowledged its cybersecurity incident had occurred at a time of “increasing cyber incidents in Australia and around the world”.
“We apologise for any concerns this may cause our customers and key stakeholders,” Coles wrote.
Information Age has contacted Australia’s cybersecurity minister Tony Burke for comment but did not receive a response prior to publication.
Woolworths gift cards reportedly drained
Coles' disclosure coincided with an unrelated cybersecurity issue at rival supermarket chain Woolworths, where customers reportedly had hundreds of dollars drained from their digital gift cards without authorisation.
ABC News said it had received numerous reports from customers across Australia who found funds on ‘Everyday Wish’ gift cards were spent by someone else – in some cases to the tune of $500.
Woolworths reportedly acknowledged the issue and confirmed it was investigating customer reports.
"We recognise the concern this has caused affected customers and we apologise to customers impacted,” a spokesperson said.
In September, Coles declared it would not renew a controversial deal with US data firm Palantir following widespread backlash over the vendor’s ties to military initiatives and the US Immigration and Customs Enforcement (ICE).