


A Queensland government department responsible for leading the state's cybersecurity efforts has revealed it lost around $800,000 during a cyberattack in the last financial year.
The Customer Services, Open Data, and Small and Family Business department (CDSB) leads the Queensland government's work in cybersecurity strategy, governance, policy and investment.
The department lost $809,000 "a result of an external cyberattack for financial gain" during the 2025-26 financial year, it confirmed in its latest annual report, released on Friday.
"No government data or sensitive information was compromised during the incident," the report read.
"The department blocked the attack and engaged a third party to mitigate any further exposure."
No payment had been made to the attackers, a CDSB spokesperson told Information Age.
"In July 2025, a third-party messaging service used by the Queensland government was misused to generate an inflated number of unauthorised SMS messages for financial gain," they said in a statement.
"... Immediate steps were taken to contain and investigate the incident, and security controls have been further strengthened."
The Queensland government "is committed to protecting the security and resilience of its systems and services", they added.
Audit found department 'needs to do more'
A report released in March by the Queensland Audit Office found CDSB "needs to do more" to effectively help the state's public sector manage third-party cybersecurity risks.
It found the department was "not actively assessing and monitoring third-party cyber capability across the public sector", but was working on improvements.
"The Queensland government has been slow to develop a framework to help entities manage their third-party cybersecurity risks," the audit suggested, adding that federal cybersecurity agency the Australian Signals Directorate (ASD) "has been raising these risks since 2021".
Auditors were also able to gain the "highest level of access" into two Queensland government entities, but did not name them so as to "avoid publicly identifying any security vulnerabilities".
CDSB referred to the audit in its annual report, stating, "In our cybersecurity leadership role, we agreed to all relevant recommendations and progressed actions during the reporting period, including initiatives to strengthen whole‑of‑government cybersecurity capability.”
Cybersecurity "remains a daily discipline" for CDSB and the Queensland government, the report said.
"Investing in, and securing Queensland’s digital assets remains important, as cyber threats become more complex, and national incident data shows that malicious actors continue to target all sectors of the economy," it said.
Queensland tops cybercrime reports
Queensland reported the highest proportion of Australia's cybercrime incidents in the 2024-25 financial year, according to ASD's latest Annual Cyber Threat Report.
The state reported 28 per cent of the nation's cybercrime incidents, closely followed by Victoria at 26 per cent and New South Wales at 22 per cent.
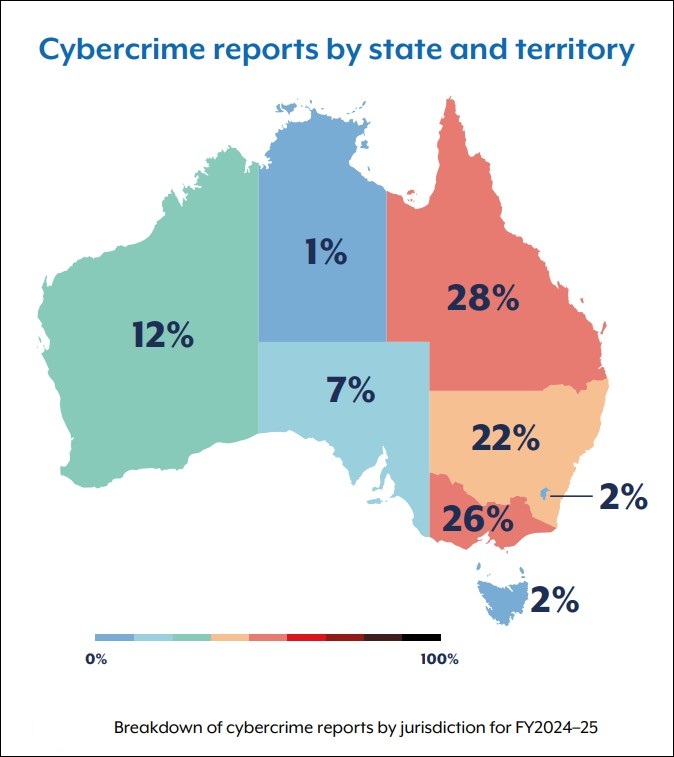
Image: ASD Annual Cyber Threat Report 2024-2025
These figures were "disproportionately higher" than the three states' respective populations, compared with other jurisdictions, ASD found.
"The Australian Capital Territory reported the highest average self-reported financial losses – around $37,700 per cybercrime report – followed by those in New South Wales, with around $33,000," the report said.
Queensland's Noosa Council lost $1.9 million to scammers who used artificial intelligence and social engineering to defraud ratepayer funds between 2024 and 2025.