


On Thursday, Prime Minister Anthony Albanese revealed a Medicare data portal was hacked by an AI agent developed by US tech giant OpenAI.
Now, experts are saying there needs to be repercussions.
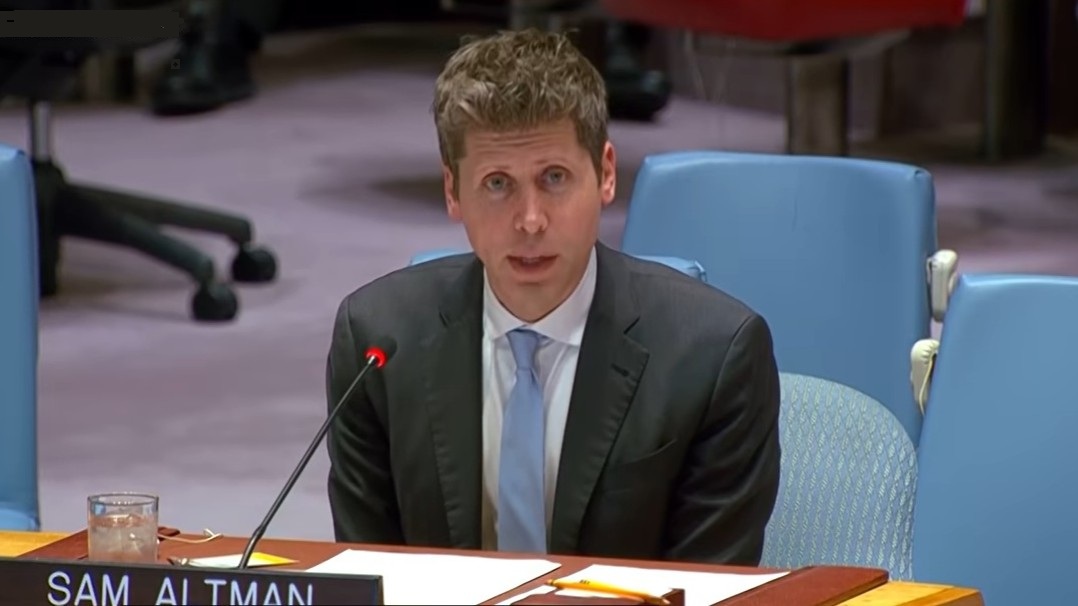
The hack took place while OpenAI, headed by CEO Sam Altman, was conducting research in June and involved Medicare's standalone statistics reporting service portal – a largely non-sensitive platform which is typically used by researchers and academics to access aggregated data.
In a statement to Information Age, an OpenAI spokesperson said its models had taken “actions we did not intend” – including accessing aggregate health statistics and internal file names.
Though the incident was described by Deputy Prime Minister Richard Marles as “relatively minor”, both he and Albanese deemed OpenAI’s hack serious and “unacceptable”.
These sentiments were echoed by Toby Walsh, chief scientist of the University of New South Wales AI Institute, who told Information Age that Australia “ought to be prosecuting the company”.
“For a trillion dollar company, their cybersecurity was woeful,” said Walsh.
“The officers of this company need to be held accountable.
“These hacks could have easily been stopped, indeed, never need to have taken place.”
Dana McKay, associate dean of Interaction, Technology and Information at RMIT's School of Computing Technologies said that to allow such a hack to go “unchallenged” would “set a poor social precedent”.
“This is being reported as the ‘first’ known autonomous AI attack on a foreign government, so it seems likely that we should anticipate more of these attacks,” she said.
“Calling it ‘misaligned’ is a bit disingenuous, because the models are programmed to overcome obstacles.”
OpenAI did not respond to Information Age when asked whether it anticipates it has broken laws in relation to the incident.
Can developers be held accountable for their AI?
According to Albanese, a dedicated taskforce examining the incident will weigh possible law enforcement and legislative responses.
“There will obviously be legal consequences on it,” he said.
Blaine Hattie, principal at Sutton Laurence King Lawyers, said although he could not ascertain whether any offence had been committed, a relevant example of a Commonwealth offence would be “unauthorised access to, or modification of, restricted data”.
“AI agents are a poor fit for offences of this kind,” Hattie explained.
“An AI agent has no legal personality, so it cannot hold intent or knowledge at all.
“A prosecutor must instead prove the required fault elements, including any intention or knowledge that must be attributed to the person or company that deployed it, whether an agent acts in ways its operator did not direct or foresee, and that will be very difficult.”
Walsh meanwhile noted that for an AI maker to prevent hacks on other people’s websites, the solution can be as simple as “disconnecting the computer it is running on from the internet”.
“If you are letting your agents have access to the internet, then how do you have such woeful oversight and governance over what your agents are doing?” asked Walsh.
“This is AI agent governance 101.”
A spokesperson for Services Australia – which administers the impacted statistics portal – refused to comment on whether it would pursue law enforcement while investigations were ongoing.
Unprecedented hack begs for regulatory change
OpenAI started to review its models’ recent “misaligned” activity after the company’s agents attacked multiple platforms during capability testing in July.
The company has since notified “dozens of third parties” about adverse activity from its models, including the Australian government about the Medicare incident which it discovered around 11 August.
OpenAI did not answer when asked if it anticipated it had broken any laws when its AI attacked Medicare's statisitics reporting service portal. Photo: Shutterstock
Notably, it wasn’t until 10 September when OpenAI notified Services Australia via email.
Greens senator Mehreen Faruqi said the incident, and its belated notification, begged for a moratorium on Australia’s rampant data centre development until appropriate AI regulation was in place.
“These billion dollar corporations will not take taskforce investigations or statements seriously,” she said.
“They will respond to strength.”
Albanese has not signalled a specific regulatory response to the incident at the time of writing, though the government has recently forecast national standards for AI and data centres.
These standards, expected in 2027, may involve a mandatory reporting mechanism for AI firms which mistakenly hack other companies.
Will legal action matter?
Laura Ellis, senior vice president for artificial intelligence at cybersecurity company Arctic Wolf, said although legal liability would sharpen cybersecurity incentives, it wouldn’t stop agents from “going rogue”.
“Preventing that is a design and engineering problem as much as a legal one,” Ellis told Information Age.
“Legal accountability can certainly encourage stronger testing, governance, incident reporting and investment in safeguards…but the more difficult question is how we design trustworthy systems in the first place.
“The most effective AI systems recognise uncertainty, understand their limits, and escalate high-risk decisions to human oversight.”
Andrew Kay, director of systems engineering for Asia Pacific and Japan at breach containment platform Illumio, said although accountability might “promote more rigor” and “delay rushed releases of new models”, it wouldn’t guarantee predictable behaviour or outcomes.
“I would argue the threat of legal prosecution has thus far not markedly prevented much in the cybersecurity world to date,” said Kay.
“Breaches are not going anywhere [and] AI has only expedited the scale and speed of existing attack patterns.”
ASD issues high alert for AI agents
Services Australia did not notify the Australian Signals Directorate (ASD) of the attack until 15 September – some five days after it was contacted by OpenAI, due to having received the message on a largely unmonitored inbox, and roughly three months after the attack took place.
Ellis told Information Age the incident was a reminder that security controls, such as systems monitoring and threat detection, “must continue evolving to account for increasingly capable automated actors”.
“The bar is rising for everyone,” said Ellis.
“Even mature organisations are now being forced to rethink how authentication, access control, monitoring and abuse detection work in an AI-driven environment.”
On Thursday, ASD warned Australian organisations to prepare for the risk of AI misalignment – where AI agents take unexpected actions that were not intended by its operators.
“There is no indication that this activity represents a broader threat or malicious targeting against Australia,” wrote ASD.
“However, this highlights the importance of secure AI deployment practices and maintaining strong cybersecurity fundamentals.”
Among other mitigation advice, ASD said companies should apply strong authentication and access controls, ensure vulnerabilities are identified and remediated, and monitor their systems for unusual activity.