

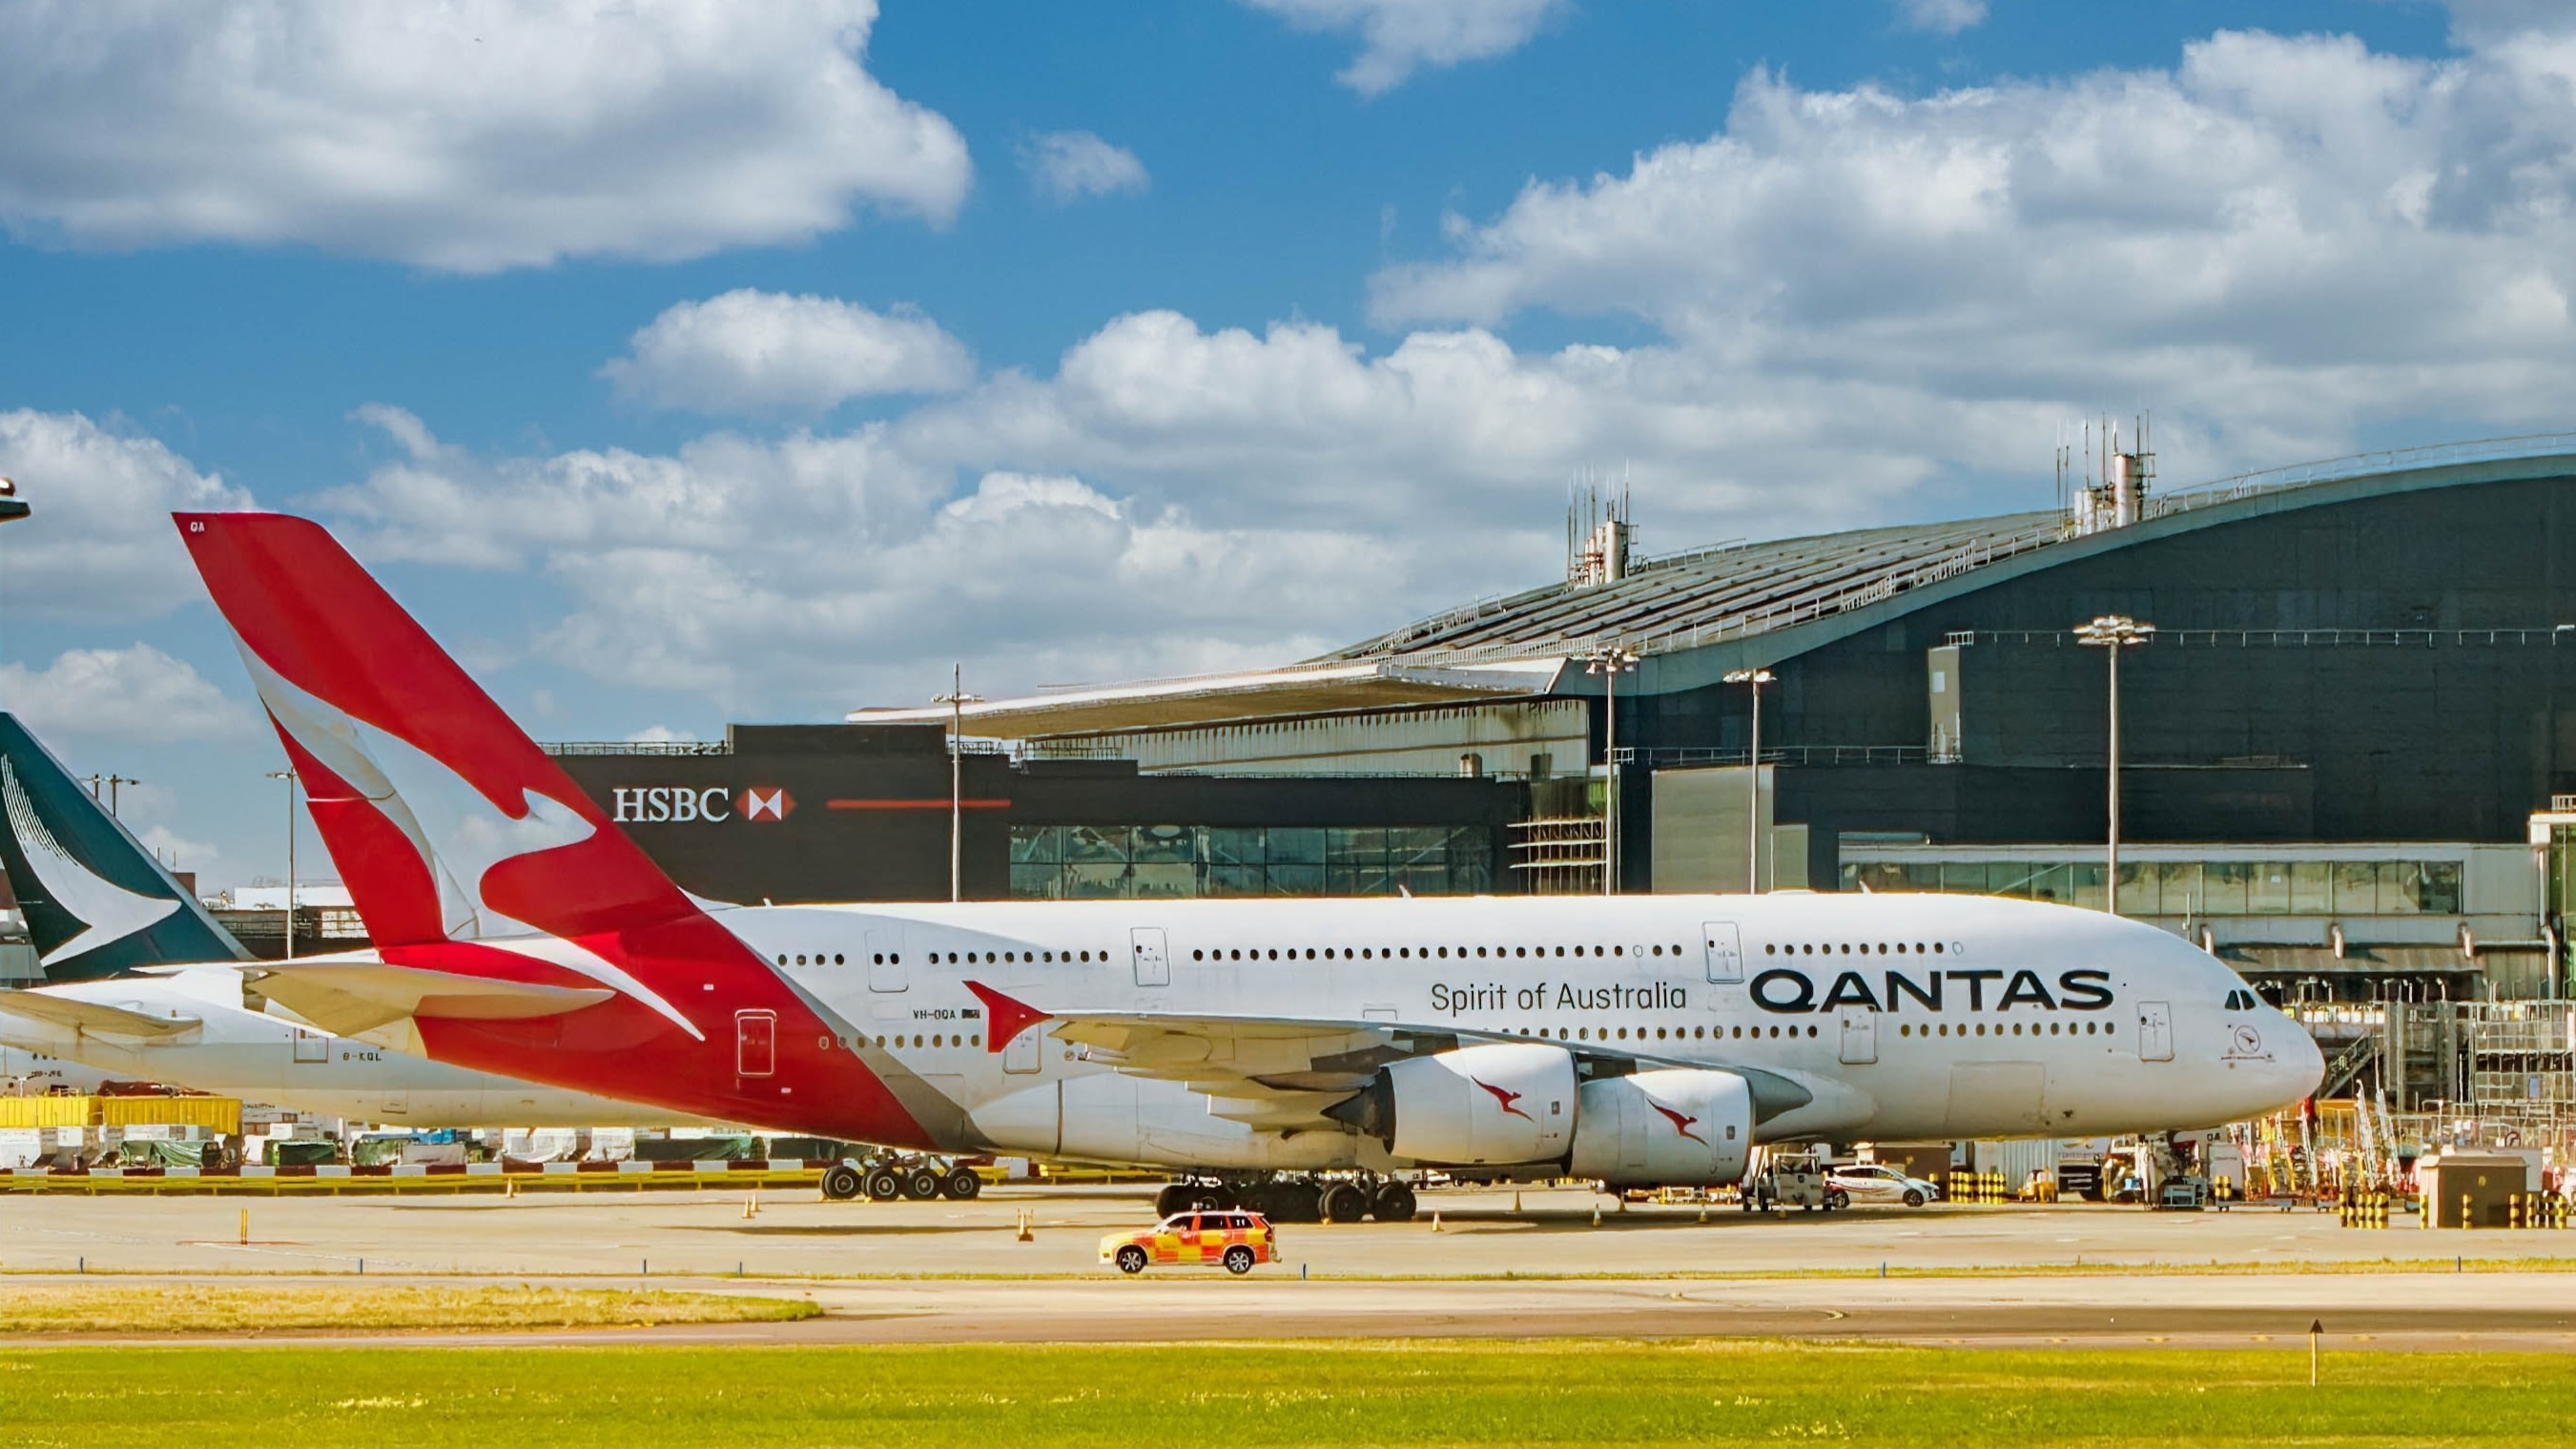

Australia’s largest airline Qantas is assessing potential data exposure after third party travel-tech provider Amadeus suffered a cyberattack impacting numerous global airlines.
Spanish travel technology provider Amadeus – which provides booking system technology and other solutions to hotels, travel companies, and more than 400 airlines – informed affected airlines of the breach in late October.
Along with Qantas, others confirmed to be affected include Singapore Airlines, Korean Air, Asiana, Japan Airlines, All Nippon Airways, and Cathay Pacific.
In a statement given to Information Age, a Qantas spokesperson said Amadeus told the airline there had been “unauthorised access” to one of the tech provider’s systems.
When asked to confirm whether any Qantas customer data was affected, a spokesperson said the airline was working with Amadeus to “understand the impact to any Qantas bookings”.
“Amadeus advised the issue was contained in September,” they said.
“There is no impact to Qantas systems or databases which remain secure.”
Qantas has notified the Australian Cyber Security Centre (ACSC) and the National Office of Cyber Security of the breach.
Booking data accessible since 2023
Amadeus said it had become aware of a “vulnerability affecting a travel booking display environment”.
Amadeus said that “certain booking-display data” was made accessible because of the flaw.
"Although our investigations continue, we can confirm that there is no evidence that payment or financial data was accessed,” Amadeus said.
“There are no indications that this vulnerability has been exploited for ransomware purposes.”
In a separate statement, Hong Kong carrier Cathay Pacific said it was told unauthorised access occurred between August 2023 and September 2026.
Cathay Pacific saw around 53,000 bookings affected by this unauthorised access, with the majority of cases involving booking references, passenger names, and flight details.
“In a smaller subset of cases, additional personal information including but not limited to email and phone contacts, travel document and/ or frequent flyer number were potentially accessed,” the Hong Kong carrier wrote.
“Amadeus has confirmed that it has taken actions to contain the incident, including a password reset, and has implemented enhanced monitoring and detection capabilities on its systems.”
According to Amadeus, the vulnerability has now been resolved.
“Amadeus implemented measures to fix the vulnerability as well as enhanced monitoring and detection capabilities,” the company said.
“We are in direct dialogue with our customers and authorities.”
Thousands of passengers affected
Malaysia Airlines confirmed the incident may have affected “certain customer information” processed through Amadeus, though it did not specify a precise number of impacted passengers.
Japan Airlines conceded approximately 90,000 customers had been impacted over the three-year period, including reservation codes, names, flight dates and whether passengers flew economy or first class.
A smaller subset of roughly 2,000 Japan Airlines customers saw their email address, phone number, passport number, nationality and/or frequent flyer numbers exposed.
All Nippon Airways similarly confirmed 37,800 customers had been affected, roughly 1,700 of which saw their passports, email addresses and other personal data exposed.
Major South Korean carriers Asiana and Korean Air also said customer reservation information had been leaked, though the full scope of the leak remains under investigation.
Third party hack puts Qantas’ reputation at risk
Last year, Qantas suffered an unrelated data breach which impacted roughly 5.12 million Australians.
Although cybercriminals eventually leaked 153GB of alleged customer data, Australia’s privacy watchdog did not find Qantas had contravened its privacy obligations.
Tracey Broers, group general manager for risk at security provider SKG Services, said the airline now faced a “clear risk of further reputational harm”.
“Customers experience the concern and inconvenience cumulatively, even where different providers or systems are involved,” said Broers.
“They want to know whether lessons from previous incidents have strengthened protection and response arrangements.”
Australian Computer Society (ACS) chief executive Prins Ralston said Qantas’ customers “deserve confidence that the information they entrust to it is protected throughout its technology supply chain”.
“Qantas says its own systems remain secure and is assessing whether bookings were affected,” said Ralston.
“But following breaches affecting Medicare, the question is urgent: how many warnings does Australia need before taking stronger control of its digital security?”
“Australians deserve more than another investigation and another apology.”
Ralston pointed to recent Australian Signals Directorate (ASD) data that showed the ACSC had responded to more than 1,500 incidents in 2025-26 – representing an increase of 20 per cent from the previous reporting period.
The directorate’s most recent annual cyber threat report also warned that malicious actors were continuing to target supply chains, and that “managing supply chain and third party risk should be a core component of any cybersecurity strategy”.
“We cannot wait for essential services to fail before demanding evidence that their protections work,” said Ralston.
“Boards and governments must insist on independent testing, clear accountability and demonstrated capability among the professionals securing and assessing these systems.”